# Cisco Threat Defense Virtual Firewall
* [Cisco Threat Defense Virtual (Formerly FTDv/NGFWv) Data Sheet.](https://www.cisco.com/c/en/us/products/collateral/security/firepower-ngfw-virtual/threat-defense-virtual-ngfwv-ds.html)
* [Cisco Secure Firewall Management Center Feature Licenses](https://www.cisco.com/c/en/us/td/docs/security/firepower/roadmap/firepower-licenseroadmap.html).
* [Cisco Firepower Version 7.0 Release Notes](https://www.cisco.com/c/en/us/td/docs/security/firepower/70/relnotes/firepower-release-notes-700.html).
**Licensing Options**
* [Bring Your Own License (BYOL)](#bring-your-own-license)
**Deployment Types**
* Single Device
* Redundant Devices
* Cluster
**Connectivity Options**
* With a Public IP Address
* Without a Public IP Address
## Device Details[](#device-details "Direct link to Device Details")
| | 4 Cores | 8 Cores | 12 Cores |
| ----------------------------------------------- | ---------------------------------------------------------------------------------------------------------------- | ------- | -------- |
| Memory | 8 GB | 16 GB | 24 GB |
| Software Package | FTDv5
FTDv10
FTDv20 | FTDv30 | FTDv50 |
| Virtual Data Interfaces Supported (Default/Max) | 10 / 10 | | |
| System Reserved Interfaces | Web-based Management (FMC, FDM or CDO) | | |
| Access Methods | SSH (CLI)
HTTPS (Web Console) | | |
| Image Version | See [Available Image Versions](https://docs.equinix.com/network-edge/vendors-devices/ne-certified-vnfs.md#cisco) | | |
| Restricted CLI Commands | None | | |
When configuring your device details, specify the following:
* Cluster Name - If you are creating a cluster, give your cluster a name.
* Device Name – Enter a name for the device. If you are creating more than a single device, `-Node 0` is appended to the primary node and `-Node 1` is appended to the secondary node after the device name.
* Device Management – Select your device management type from the following:
* Firewall Management Center (FMC) – Enter the FMC’s IP Address as the *Controller IP Address*, and the *Registration Key*. The registration key is used to register the device to the FMC.
* Firepower Device Manager (FDM)
* Cisco Defense Orchestrator (CDO)
* SSH Access - Unlike the other VNF types, we do not provide username and RSA Public Key configuration settings for SSH access during the device creation workflow. Use console access from the device details page.
## Deploying Without IP Address[](#deploying-without-ip-address "Direct link to Deploying Without IP Address")
* When the connectivity type **Without Equinix Public IP Address** is selected, the VNF is provisioned without a public IP Address on the WAN or Management interface. You are responsible for configuring the license registration, overlay network configuration, and clustering (optional).
The following is an example (reference only) command for management interface setup.
```
configure network ipv4 manual
```
* Clustering - The option to deploy a cluster is not available if you are not using public IP addresses. You must configure cluster devices manually.
## Bring Your Own License[](#bring-your-own-license "Direct link to Bring Your Own License")
If you are Bringing Your Own License (BYOL), the following device creation steps will apply:
* You can enter your License Token during the device creation process. Once you enter the license token, your virtual device will be provisioned with the license based on the token provided. If you do not provide token information, your virtual device will still be provisioned but you will need to manually register your license with the smart server using your license token after the virtual device is provisioned.
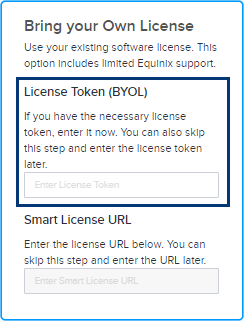
* Alternatively, you can enter your Smart License URL. You must have a valid Cisco account to complete this process. To get a Cisco Smart License token, follow the instructions in the [Cisco documentation](https://www.cisco.com/c/en/us/support/docs/licensing/common-licensing-issues/how-to/device-management/lic220943-how-can-i-create-a-token-to-register-my.html).
To get a Cisco Smart License token:
* Sign in to the Cisco Smart Software Manager (CSSM) with your Cisco.com account credentials.
* Locate the *Virtual Accounts* > *Inventory* section to create a new token.
* Your newly created token will appear in the token list. Click the token to see the details and copy the token string.
To register the new token on your device, access the device CLI and enter a command to register your token.
```
license smart register idtoken
```
To verify your token registration enter a command such as:
```
show license status
```
If you encounter any issues or need more detailed steps, see [Cisco DNA Center Administrator Guide](https://www.cisco.com/c/en/us/support/cloud-systems-management/dna-center/products-maintenance-guides-list.html) or contact Cisco support.
* You are responsible for obtaining support from Cisco or their partners. If you are subscribing with a license from Equinix Network Edge, you can open a support case with Cisco Technical Assistant Center (TAC) to troubleshoot Cisco IOX-XE software issues or ask Cisco IOX-XE configuration questions from the Network Edge portal. See [Cisco Catalyst 8000V Subscriptions](https://docs.equinix.com/network-edge/vendors-devices/cisco/ne-cisco-8000v-specs.md#cisco-catalyst-8000v-subscriptions) for more information.