# Cisco Meraki vMX SD-WAN (Beta)
> **Note**
>
> Cisco Meraki vMX on Network Edge is currently available as a Beta offering only.
The Meraki vMX is a virtual instance of the Meraki MX security and SD-WAN appliance. It brings Auto VPN, secure connectivity, and cloud-managed control to your Network Edge footprint, all from the Meraki Dashboard. Deploy it in an Equinix metro and extend your Meraki SD-WAN fabric to the cloud and to your colocation environment.
**Licensing Options**
Meraki vMX is available on Network Edge with BYOL only. You are responsible for purchasing and managing your Meraki licenses and a device-level support contract with Cisco Meraki. Equinix support is limited to Network Edge infrastructure.
Each vMX requires its own license in your Meraki organization. To purchase licenses, contact your Cisco Meraki reseller or sales representative before you create the device.
**Deployment Types**
* Single Device
* Redundant Devices
**Connectivity Options**
* With Equinix Public IP Address
* Without Equinix Public IP Address
## Create a Meraki vMX[](#create-a-meraki-vmx "Direct link to Create a Meraki vMX")
### Prerequisites[](#prerequisites "Direct link to Prerequisites")
Before you create a Meraki vMX, make sure you have:
* An Equinix account with the `Network Edge Device Manager` role and a global billing account or a local billing account for the target metro.
* A Meraki Dashboard account with an organization that has a valid vMX license.
* A design for your network: IP addressing plan, VLAN assignments, and Auto VPN topology (hub or spoke).
* For devices without a public IP address, a helper device (a router or firewall) that provides DHCP and NAT, see [Configuring a Meraki vMX Without a Public IP Address](https://docs.equinix.com/network-edge/vendors-devices/cisco/cisco-meraki-without-IP.md).
### Prepare the Meraki Dashboard[](#prepare-the-meraki-dashboard "Direct link to Prepare the Meraki Dashboard")
Before beginning the device deployment process in Network Edge:
1. Create an account in the [Meraki Dashboard](https://account.meraki.com/login).
2. Sign in to the dashboard and create a new Organization and Network, selecting **Security appliance** as the network type.
3. Choose the required Meraki vMX device size.
4. On the device page, select **Generate authentication token** to create the Day-0 configuration file. If you are creating redundant devices, create separate Day-0 tokens for each device.
> **Important**
>
> Do not generate the Meraki Day-0 token until you are ready to create the vMX. The token is valid for one hour.
### Create the Device[](#create-the-device "Direct link to Create the Device")
1. Sign in to the [Equinix Customer Portal](https://portal.equinix.com/) and go to the Network Edge Dashboard.
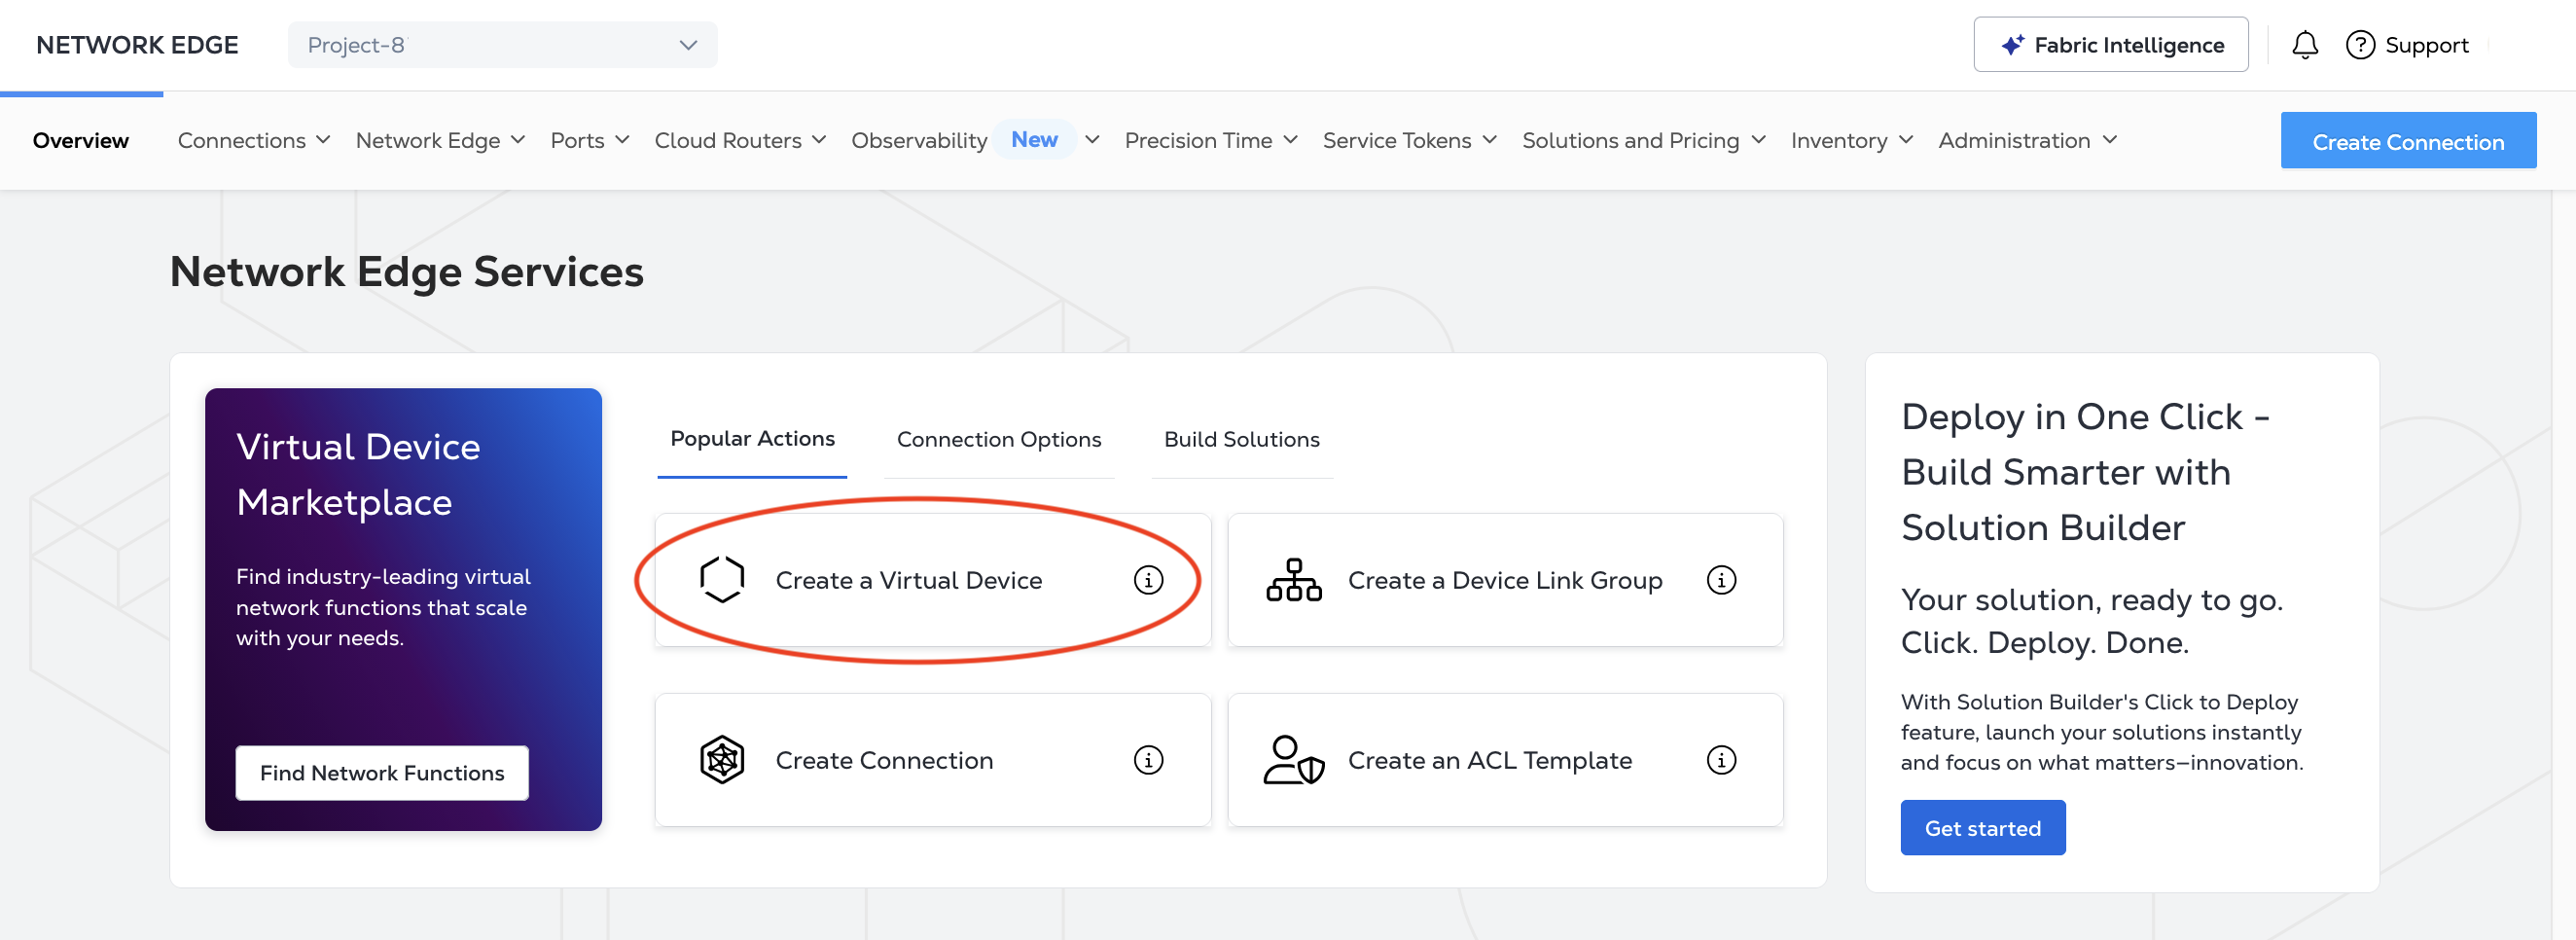
2. Click **Create a Virtual Device**.
3. In the vendor package section, locate the Meraki vMX card and click **View Details**.
4. Click **Select and Continue**.
5. Review the [prerequisites](#prepare-the-meraki-dashboard) and click **Create SD-WAN Device**.
6. In the **Deployment Type** section, click **Single**.
7. Click **Begin Creating Edge Devices**.
8. Select a Metro.
9. Select a Billing Account or [create a new billing account](https://docs.equinix.com/network-edge/billing/ne-billing-account-creation.md).
10. Click **Next: Device Details**.
11. In the **Connectivity Option** section, select **With Equinix IP Address** or [**Without an Equinix IP Address**](https://docs.equinix.com/network-edge/vendors-devices/cisco/cisco-meraki-without-IP.md).
12. Select the [**Device Resources**](#meraki-vmx-specifications).
13. In the **Device Details** section enter:
* **Device Name** - Enter a name for your device.
* **Host Name Prefix** - Enter the host name prefix.
* **Token** - Paste the Day-0 authentication token created during the [Prepare the Meraki Dashboard](#prepare-the-meraki-dashboard) process.
> **Info**
>
> The default number of interfaces is 2, so there is no selection to make in the **Interfaces** drop-down.
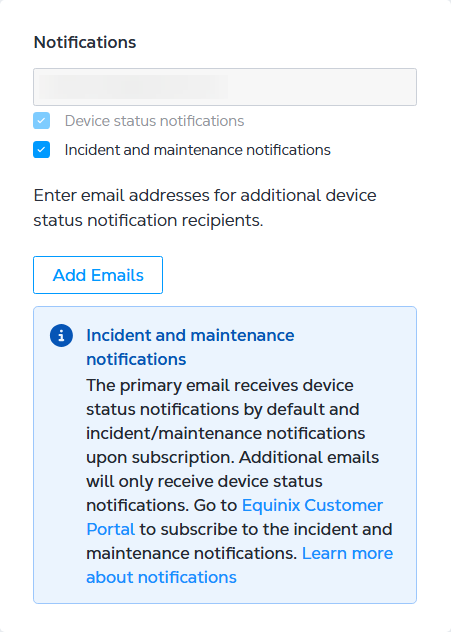
14. Your email address will automatically populate the **Notifications** field as the person who will receive all notifications about the device. Click **Add Emails** to add the email addresses of anyone else who should receive notifications.
15. Select a purchase order in the **Purchase Order Number** drop-down.
16. (Optional) Enter an **Order Reference/Identifier** for the device.
17. Click **Next: Additional Services**.
18. In the **Device Access** section, enter your username.
19. Select **Set up SSH with RSA Public Key** to generate an RSA key.
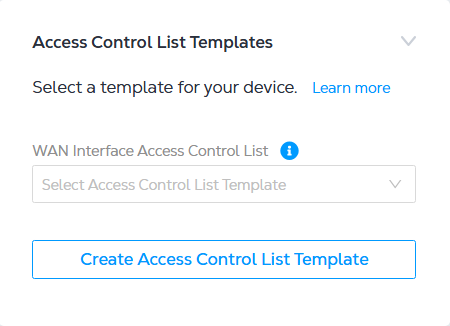
20. In the **Access Control List Templates** section, select an existing ACL template to apply to your device, or click Create Access Control List Template to create a new template.
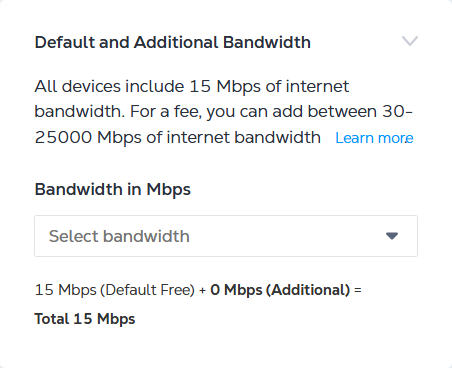
21. In the **Default and Additional Bandwidth** section, select additional bandwidth in the drop-down if you want to add bandwidth to the default 15 Mbps of internet bandwidth that comes with your device deployment.
22. Click **Next: Review**.
23. In the Shared Support section, click **I have reviewed this support policy and acknowledge it.**.
24. Click **Create Virtual Device**.
## Meraki vMX Specifications[](#meraki-vmx-specifications "Direct link to Meraki vMX Specifications")
| | |
| ------------------------------ | --------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Device Resources | 2 Cores - 4 GB (supports vMX Small)
4 Cores - 16 GB (supports vMX Medium and vMX Large) |
| Software Package | vMX - Small
vMX - Medium
vMX - Large |
| Interfaces Supported (Default) | 2 |
| Access Methods | Meraki Dashboard |
| Connectivity | With Equinix Public IP Address
[Without Equinix Public IP Address](https://docs.equinix.com/network-edge/vendors-devices/cisco/cisco-meraki-without-IP.md) |
| Image Version | See [Available Image Versions](https://docs.equinix.com/network-edge/vendors-devices/ne-certified-vnfs.md#cisco) |
| RMA | Supported |
| Snapshot | Not Supported |
| Resize | Supported |
## Verify the Deployment[](#verify-the-deployment "Direct link to Verify the Deployment")
In the Meraki Dashboard, select Security & SD-WAN > Monitor > Appliance status. Confirm the vMX is online. Allow about five minutes after the link is active.
In the [Equinix Customer Portal](https://portal.equinix.com/), confirm both devices are Provisioned and the device link group is active.
## Support and Resources[](#support-and-resources "Direct link to Support and Resources")
### Troubleshooting[](#troubleshooting "Direct link to Troubleshooting")
If the vMX is not visible in the Meraki Dashboard:
* **Token expired** - The Day-0 token must be used within one hour of generation. Generate a new token in the Meraki Dashboard.
* **Device not provisioned** - Confirm the device status is `Provisioned` in the Virtual Device Inventory.
* **ACL blocks required traffic** - Review the ACL template applied to the device. For a helper device, make sure return traffic from the Meraki cloud is permitted.
- [Getting Started with Meraki](https://documentation.meraki.com/Getting_Started_with_Meraki)
- [vMX Comparison Datasheet](https://documentation.meraki.com/SASE_and_SD-WAN/MX/Install_and_Get_Started/Installation_Guides/vMX_Comparison_Datasheet)
- [Meraki Security and SD-WAN Licensing](https://documentation.meraki.com/Platform_Management/Product_Information/Licensing/Meraki_MX_Security_and_SD-WAN_Licensing)